A Cybersecurity Assessment Found 47 Issues. What Should You Do First?
EXECUTIVE INSIGHT
Cybersecurity assessments can be valuable.
They can identify vulnerabilities, control weaknesses, missing policies, configuration issues, process gaps, and areas where an organization may not meet a particular security requirement.
But an assessment can also leave business leaders with a new problem:
What do we do with all of these findings?
A report containing dozens of recommendations may provide useful information without providing enough clarity about what the business should actually do next.
Not Every Finding Has the Same Business Importance
A technical finding may be significant from a cybersecurity perspective.
But deciding what to do about it requires additional context.
What business operation does it affect?
Which information and systems does this issue affect?
Could it affect an important customer?
Is there an insurance, contractual, or regulatory requirement?
Could it disrupt operations?
How difficult or expensive would it be to address?
What happens if the organization accepts the risk for now?
Those questions begin moving the conversation from a list of technical findings to business decisions.
Priority Should Begin With the Business
For a small or mid-sized business, cybersecurity resources are rarely unlimited.
Time, people, budget, and management attention all compete with other business priorities.
That makes prioritization essential.
The objective shouldn’t simply be to close the largest possible number of findings.
Leadership should identify which issues matter most to the business, decide what to address first, and make informed decisions about the rest.
Sometimes a relatively simple issue deserves immediate attention because of its potential business impact.
Another technically significant issue may require a longer-term solution.
The business may reduce some risks by using an existing capability.
Leadership may consciously accept others.
The right answer depends on the business context.
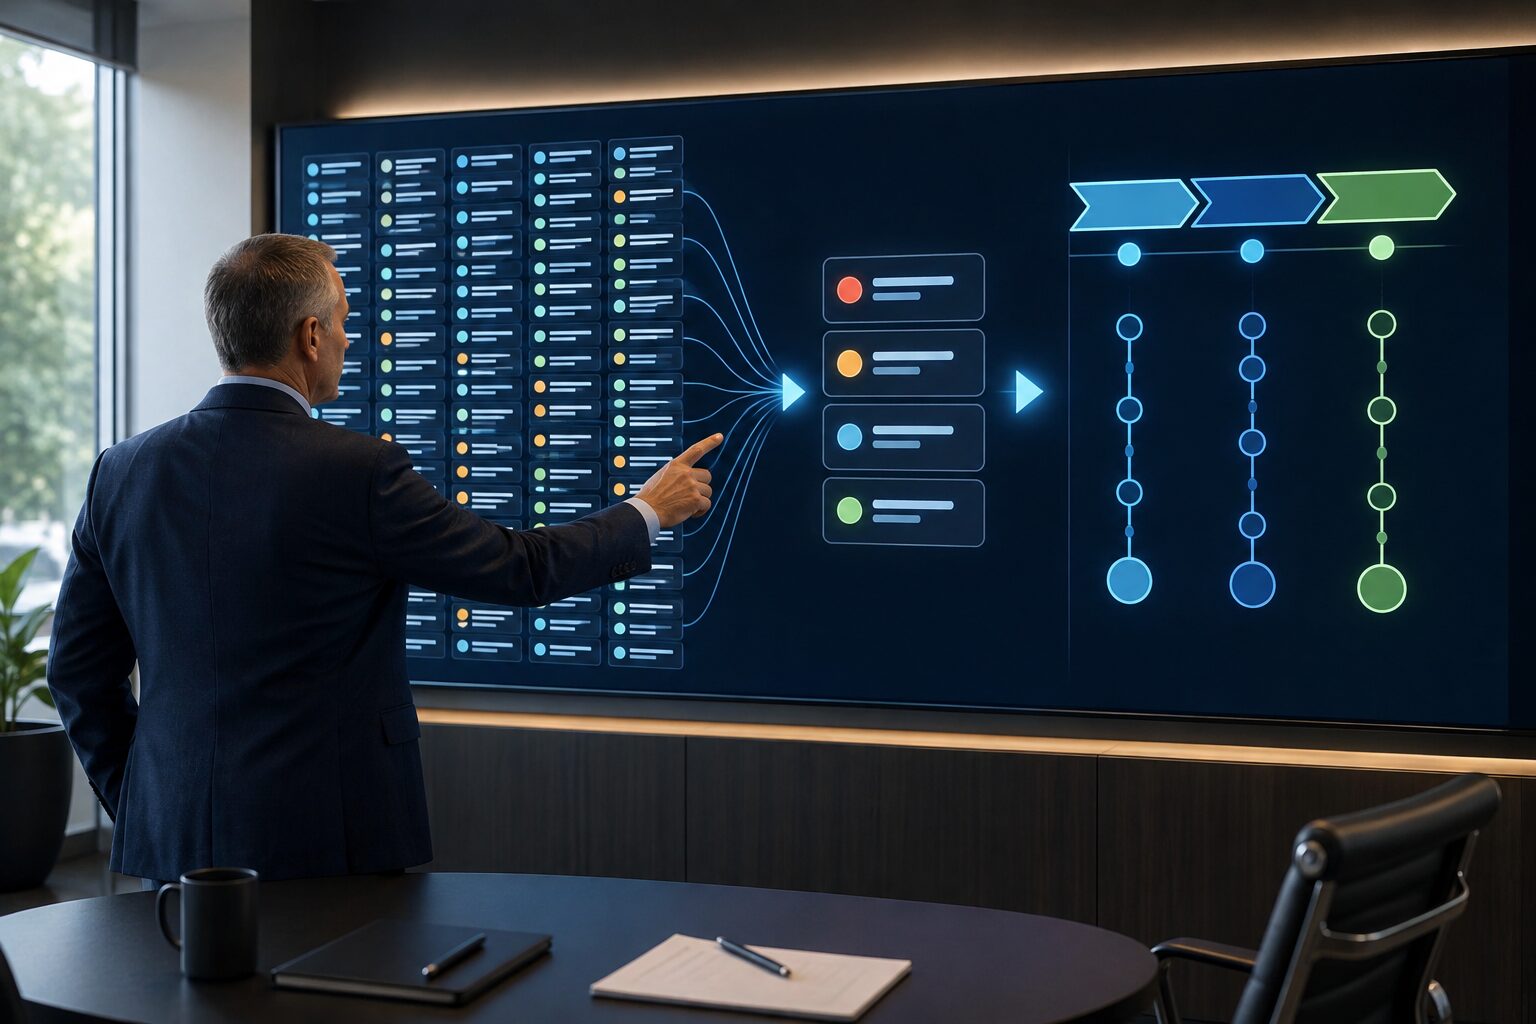
From Findings to Decisions
A useful cybersecurity assessment should help leadership move beyond:
We found these problems.
Toward:
What matters most.
Why it matters to the business.
What we recommend addressing first.
The decisions leadership needs to make.
A practical path forward.
That transition matters because delivering a report does not improve cybersecurity.
It happens when the organization can make and execute informed decisions based on what the report uncovered.
The Roadmap Matters as Much as the Assessment
Once leadership establishes priorities, the findings can form the foundation for a practical cybersecurity roadmap.
The roadmap should not assume the organization will fix everything immediately.
It should help leadership understand what needs attention now, what can follow, what dependencies exist, and where investment is likely to create the greatest business value.
It should also evolve as the business changes.
New customers, systems, employees, acquisitions, insurance requirements, regulations, threats, and business objectives can all change cybersecurity priorities.
A roadmap therefore shouldn’t become another static document sitting on a shelf.
Create Something the Business Can Continue to Use
This is where the concept of Reusable Business Protection Assets™ (RBPAs™) becomes important.
The value of an assessment shouldn’t disappear when the engagement ends.
Where appropriate, the organization can govern assessment findings, leadership decisions, priorities, and the resulting roadmap as business assets, then maintain, update, adapt, and reuse them.
The principle is simple:
Create once. Govern it. Adapt it. Reuse it. Retain its value.
Instead of repeatedly starting over, the organization builds on decisions and work it has already completed.
Better Decisions Are the Outcome
The goal of a cybersecurity assessment isn’t simply to identify more problems.
It is to give leadership enough clarity to make better decisions about cybersecurity risk.
That means understanding:
What matters most?
Why does it matter?
What should we do first?
Where should we invest?
What can wait?
What risk are we willing to accept?
That is Executive Cyber Clarity™.
More cybersecurity doesn’t mean less risk.
Better decisions do.
Start With a Conversation
If your organization has completed a cybersecurity assessment—or has a collection of findings and recommendations but isn’t sure what to address first—BriarArc Cyber can help turn that information into clear priorities and a practical path forward.