More Cybersecurity Doesn’t Mean Less Risk. Better Decisions Do.
EXECUTIVE INSIGHT
For many business leaders, cybersecurity has become increasingly difficult to understand.
At the same time, the volume keeps growing: more security products, alerts, assessments, compliance requirements, vendors, and recommendations. All of them compete for attention and budget.
Yet one fundamental question often remains unanswered:
Are we making the right cybersecurity decisions for our business?
That question is at the heart of Executive Cyber Clarity™.
Business leaders should not measure cybersecurity by how many tools a company owns or how much technology it deploys. They should measure it by how effectively the business understands its most important risks, makes informed decisions about those risks, and protects what matters most.
The Cybersecurity Problem Is Often a Decision Problem
Growing businesses rarely suffer from a lack of cybersecurity information.
They receive information from technology providers, insurance companies, customers, regulators, security assessments, employees, and outside advisors.
The challenge is determining what matters.
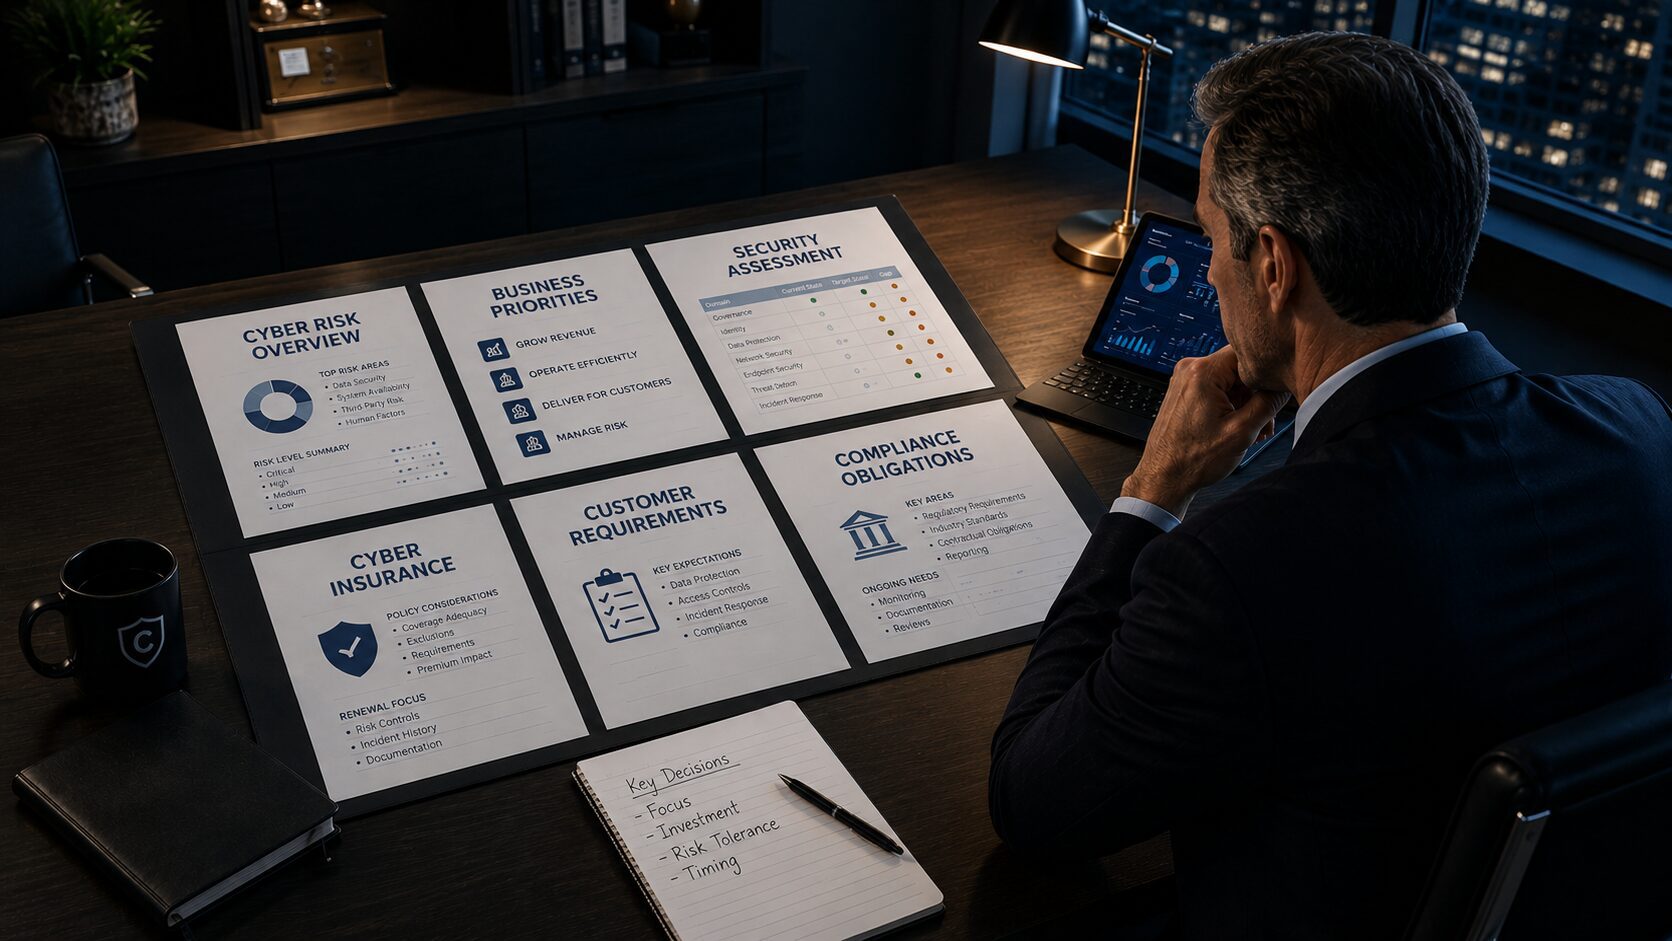
A business leader may simultaneously receive recommendations to strengthen identity protection, improve backups, address vulnerabilities, implement employee training, satisfy a customer’s security requirements, prepare for a cyber insurance renewal, and improve incident response.
Every recommendation may have merit. But they are not necessarily equally important.
Without business context and clear priorities, cybersecurity can quickly become a series of disconnected investments rather than a coordinated business strategy.
Start With the Business, Not the Technology
Effective cybersecurity begins with understanding the business.
What operations are essential?
What information would create the greatest business impact if criminals stole or exposed it, or if the business could no longer access it?
Which systems are critical to serving customers?
What contractual, regulatory, insurance, or customer requirements must the company satisfy?
What would happen if a ransomware attack disrupted operations tomorrow?
Only after answering questions like these can leaders evaluate cybersecurity priorities against the needs of the business.
That changes the conversation from:
“What security technology should we buy?”
to
“What business risks should we address first?”
That distinction matters.
Cybersecurity Is a Business Investment
Every business has limited resources.
Business leaders must allocate time, capital, people, and executive attention carefully. Cybersecurity is no exception.
The objective isn’t to eliminate every possible cyber risk. That isn’t realistic.
The objective is to understand which risks could materially affect the business and make deliberate decisions about how to address them.
Some risks may require immediate action.
Leadership may reduce other risks over time.
The business may transfer some risks through insurance or contractual arrangements.
Leadership may consciously accept some risks.
The important point is that these should be business decisions, not accidental outcomes created by disconnected technology choices.
From Cybersecurity Complexity to Executive Cyber Clarity™
This is why we created BriarArc Cyber.
We help business owners and executives understand cybersecurity in business terms so they can make informed decisions about risk, priorities, and investment.
We call that Executive Cyber Clarity™.
It means helping leadership understand:
what matters most to the business;
where meaningful cyber risk exists;
which actions deserve priority;
where cybersecurity investment will have the greatest business impact; and
what decisions leadership needs to make next.
The result should not be more cybersecurity for the sake of cybersecurity.
It should be better business protection through better decisions.
More Cybersecurity Doesn’t Mean Less Risk.
Better Decisions Do.
That belief is the foundation of BriarArc Cyber Executive Insights.
We will examine practical cybersecurity issues affecting growing businesses—not simply from the perspective of technology, but from the perspective of the executives responsible for protecting and growing the business.
Because the most important cybersecurity question isn’t:
“Are we doing more?”
It is:
“Are we making the right decisions?”
Start With a Conversation
If you’re trying to determine where your business should focus its cybersecurity attention and investment, BriarArc Cyber can help bring clarity to the decisions ahead.